Active TS/SCI · DoD 8570 IAT II

Secure cloud infrastructure for defense programs.

I build and harden Terraform-provisioned infrastructure at IL5 across Azure Government and AWS GovCloud — STIG baselines, the automation that keeps them applied, and CI/CD pipelines with security gates that actually block.

Active TS/SCIcurrent clearance
DoD 8570 IAT IISecurity+ CE
IL5 EnvironmentsAzure Gov · AWS GovCloud
Terraform · GitLab CIIaC and pipeline delivery
What I do

Build it as code, then prove it's hardened

Infrastructure work in accredited environments has two halves: standing the thing up, and being able to demonstrate it meets the controls. I do both, and I document them so the next engineer doesn't start from zero.

infrastructure/as-code

Infrastructure as code at IL5

Terraform modules provisioning workloads across Azure Government and AWS GovCloud. Remote state with locking, reusable module patterns promoted between environments, and sovereign-endpoint configuration handled correctly rather than assumed.

TerraformAzure GovernmentAWS GovCloudIL5
hardening/compliance

STIG hardening and compliance automation

Applying DISA STIG baselines to systems, running vulnerability scans, remediating findings, and documenting residual risk. The harder half is keeping it applied — automation that detects and corrects drift against mandated baselines rather than a one-time pass.

DISA STIGVulnerability scanningNIST 800-53NIST 800-171
pipelines/ci-cd

CI/CD pipelines and platform migration

Building and maintaining GitLab CI pipelines, and migrating GitLab instances — including across disconnected boundaries with no network path between source and target, handled programmatically through the REST API. Policy-as-code gates on both GitLab and GitHub Actions.

GitLab CIGitHub ActionsCheckovPython
identity/zero-trust

Identity and Zero Trust

Entra ID and Active Directory across multi-tenant environments: attribute-based access control, Privileged Identity Management, Conditional Access deployed as code, and CAC/PKI certificate provisioning in IL5.

Entra IDABACPIMCAC / PKIGraph API
Selected work

Four platforms, built and documented

Each of these was designed, deployed, and debugged end to end. Where source is public it's linked; the rest are private, and I'm glad to walk through any of them in detail.

Azure DevSecOps Pipeline

view source ↗
TerraformCheckovOIDC FederationEntra IDDefender

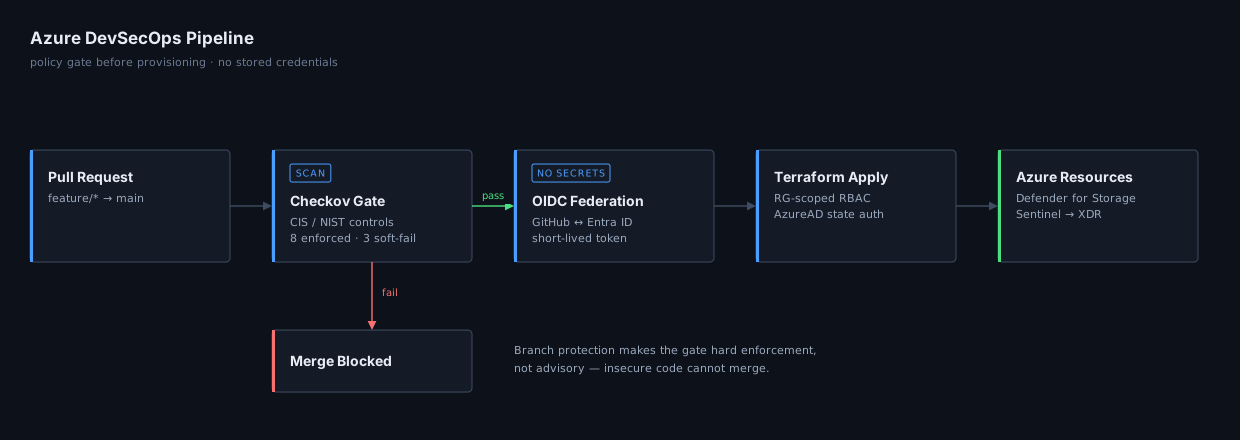
A shift-left pipeline that blocks insecure Terraform before it ever reaches Azure. Branch protection makes the Checkov gate hard enforcement rather than advisory, and deployment authenticates through OIDC federation — no stored secrets, nothing to rotate.

  • 11 Checkov controls per run; 8 enforced, 3 soft-failed with written justification — a security decision, not a bypass
  • GitHub mints a short-lived token at runtime; Entra ID exchanges it. Service principal scoped to one resource group, not the subscription
  • Terraform state in Azure Blob using AzureAD auth — use_azuread_auth on the backend block, because the provider env var alone doesn't propagate to backend init
Architecture diagram: pull request flows into a Checkov policy gate; failures block the merge, passes proceed through OIDC federation to a resource-group-scoped Terraform apply.

AWS Container Platform — ECS Fargate

Private source
TerraformECS FargateECRALBIAM

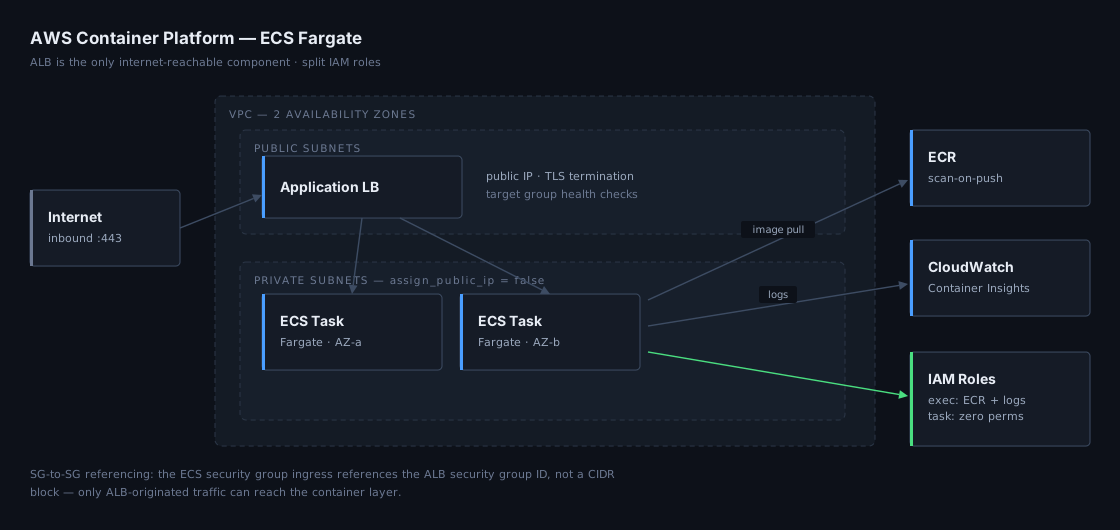
A production-pattern containerized platform, entirely Terraform-provisioned with no manual console steps. Tasks run exclusively in private subnets; the load balancer is the only internet-reachable component in the account.

  • Two separate least-privilege IAM roles that are never combined — the execution role pulls from ECR and writes logs, the task role holds zero AWS permissions, so a compromised container gains nothing
  • Security-group-to-security-group ingress referencing the ALB's group ID rather than a CIDR block, so only ALB-originated traffic reaches containers
  • Debugged a real ARM64/AMD64 mismatch — building on Apple Silicon requires docker buildx --platform linux/amd64 for Fargate compatibility
Architecture diagram: a VPC across two availability zones with an Application Load Balancer in public subnets routing to ECS Fargate tasks in private subnets, pulling images from ECR and writing to CloudWatch under split IAM roles.

Zero Trust Conditional Access Stack

Private source
Terraformazuread providerEntra IDGCC High

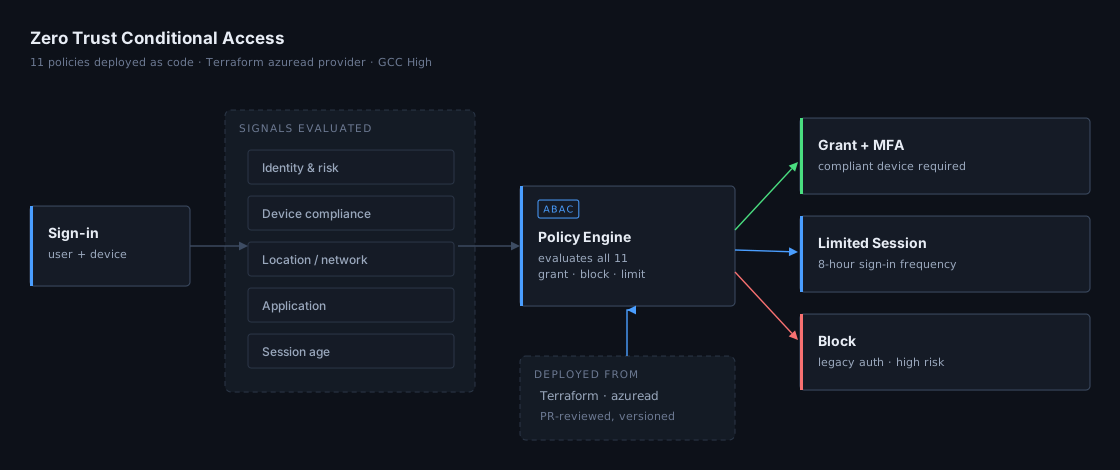
Eleven Conditional Access policies deployed entirely as code. Treating the identity control plane as infrastructure means every access decision is version-controlled, peer-reviewable, and reproducible across tenants.

  • Full baseline: MFA enforcement, legacy auth block, device compliance gating, privileged role MFA, risk-based policies, guest MFA, and sign-in frequency limits on sensitive apps
  • Variables-driven throughout — break-glass group, service account exclusions, privileged role IDs and app IDs are all inputs, never hardcoded
  • Safe promotion path: deploy in report-only mode, review sign-in logs, then enforce
Architecture diagram: a sign-in attempt is evaluated against identity, device, location, application and session signals by a policy engine, resulting in grant with MFA, a limited session, or a block — with all policies deployed from Terraform.

Azure SSH Honeypot & Detection Pipeline

Private source
TerraformCowrieLog AnalyticsSentinelKQL

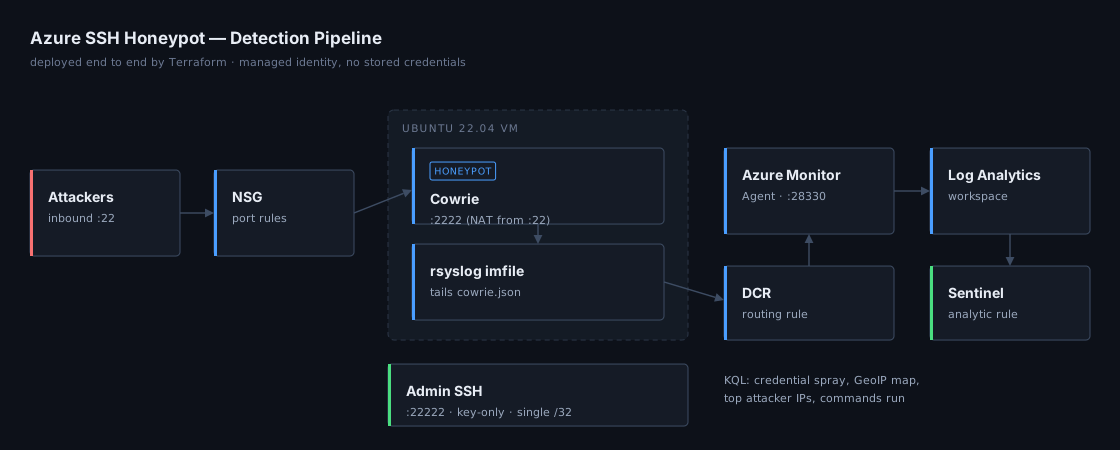
A deliberately exposed SSH honeypot that attracts real attack traffic and surfaces attacker behavior through Azure-native tooling. Deployed end to end in one terraform apply — VM, networking, log pipeline, Sentinel onboarding, and the analytic rule.

  • Port 22 is open to the internet; real admin SSH sits on 22222, key-only, restricted to a single /32 via NSG
  • Log pipeline from Cowrie through rsyslog imfile to the Azure Monitor Agent TCP collector and into Log Analytics, authenticated by managed identity with no stored credentials
  • KQL powering credential-spray detection, a GeoIP attack map, top attacker IPs, and the commands attackers actually ran
Architecture diagram: internet attackers hit an NSG-filtered VM running Cowrie, whose logs flow through rsyslog and the Azure Monitor Agent via a data collection rule into Log Analytics and a Sentinel analytic rule.

Full case-study index, including work not shown here → github.com/ekaumoh/lets-build

Credentials

Certifications and clearance

Active TS/SCI Security ClearanceActive
CompTIA Security+ CE — DoD 8570 IAT IIActive
Microsoft Azure Fundamentals (AZ-900)Active
CompTIA A+Active
SC-300 — Identity and Access AdministratorIn progress
AZ-500 — Azure Security Engineer AssociateIn progress
AZ-140 — Azure Virtual Desktop SpecialtyIn progress
AWS Certified Security — SpecialtyPlanned
Get in touch

Let's talk

Open to conversations about cloud security, identity, and platform engineering roles in the federal and defense space.

  • Active TS/SCI — cleared on day one
  • DoD 8570 IAT II compliant
  • Silver Spring, MD · open to remote and hybrid

or email direct → admin@ekaetteumoh.cloud